Select a hunt to review its evidence.
Each hunt keeps its screenshots and video status inside its own expandable case file.
Hunt 01Video pendingCrowdStrike · Adversary-led huntHunting SOLAR SPIDER with CrowdStrike Falcon
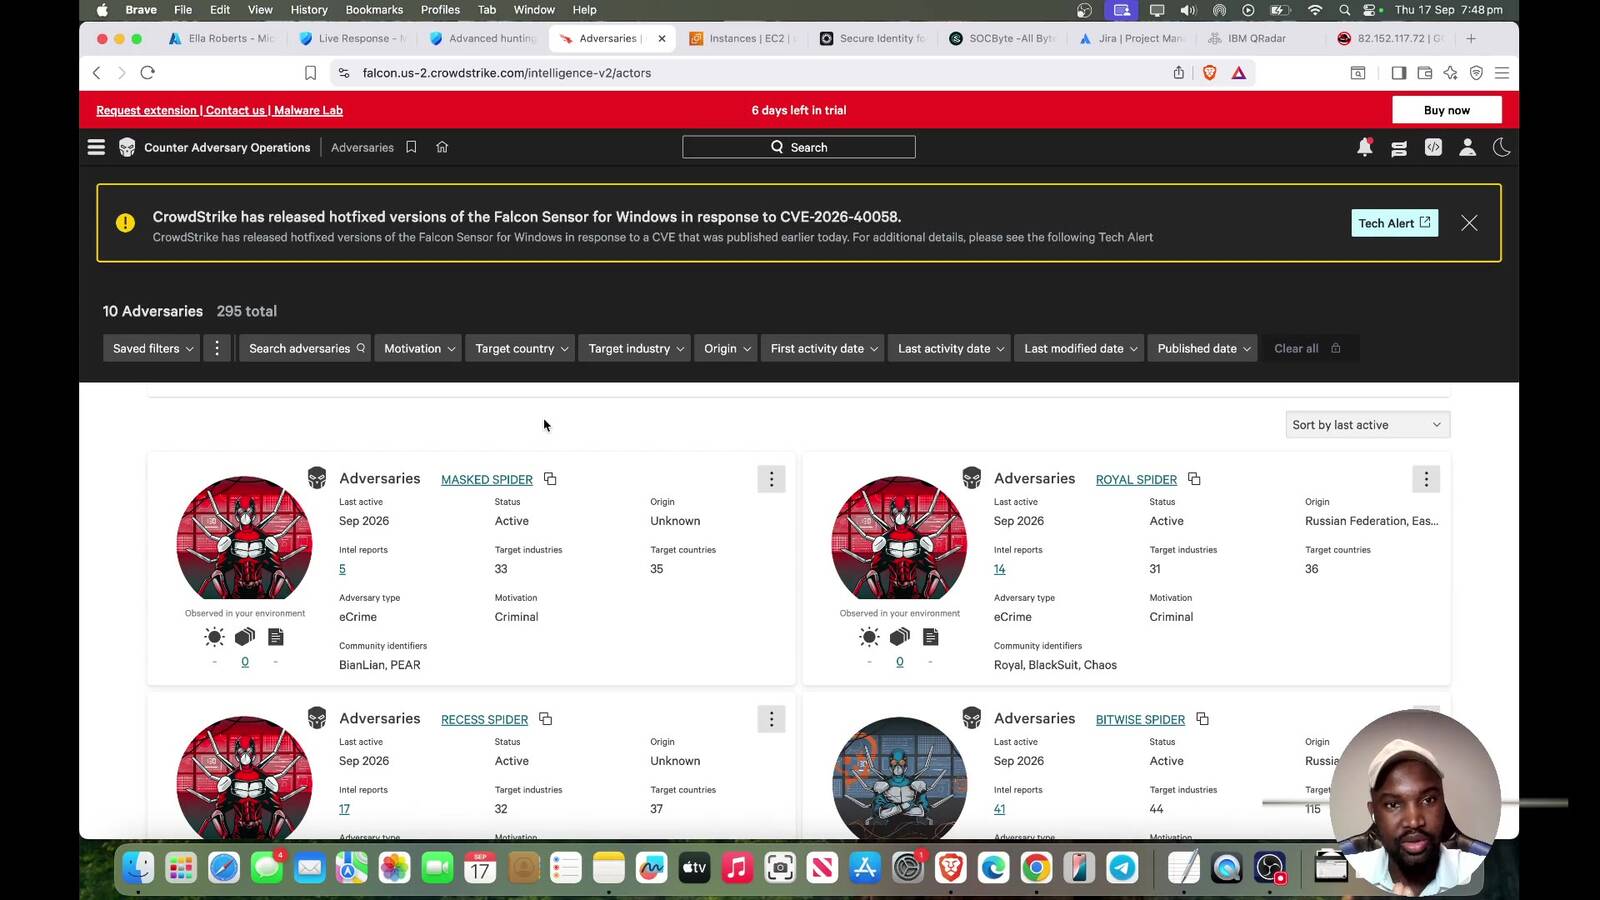
I used CrowdStrike Falcon Intelligence to review adversary profiles and translate threat intelligence into endpoint hunting pivots.
Click to view Hunt 01 evidence ↓
Hunting SOLAR SPIDER with CrowdStrike Falcon
I used CrowdStrike Falcon Intelligence to review adversary profiles and translate threat intelligence into endpoint hunting pivots.
Adversary profile → documented techniques → observable endpoint behaviors → process and host pivots → prevalence review.
Use intelligence to guide the hunt while keeping attribution separate from confirmed environmental evidence.
Open SOLAR SPIDER project & preview →
Hunt 02Video pendingDefender XDR · Ransomware behavior huntRansomware Precursors → Endpoint & Identity Hunt
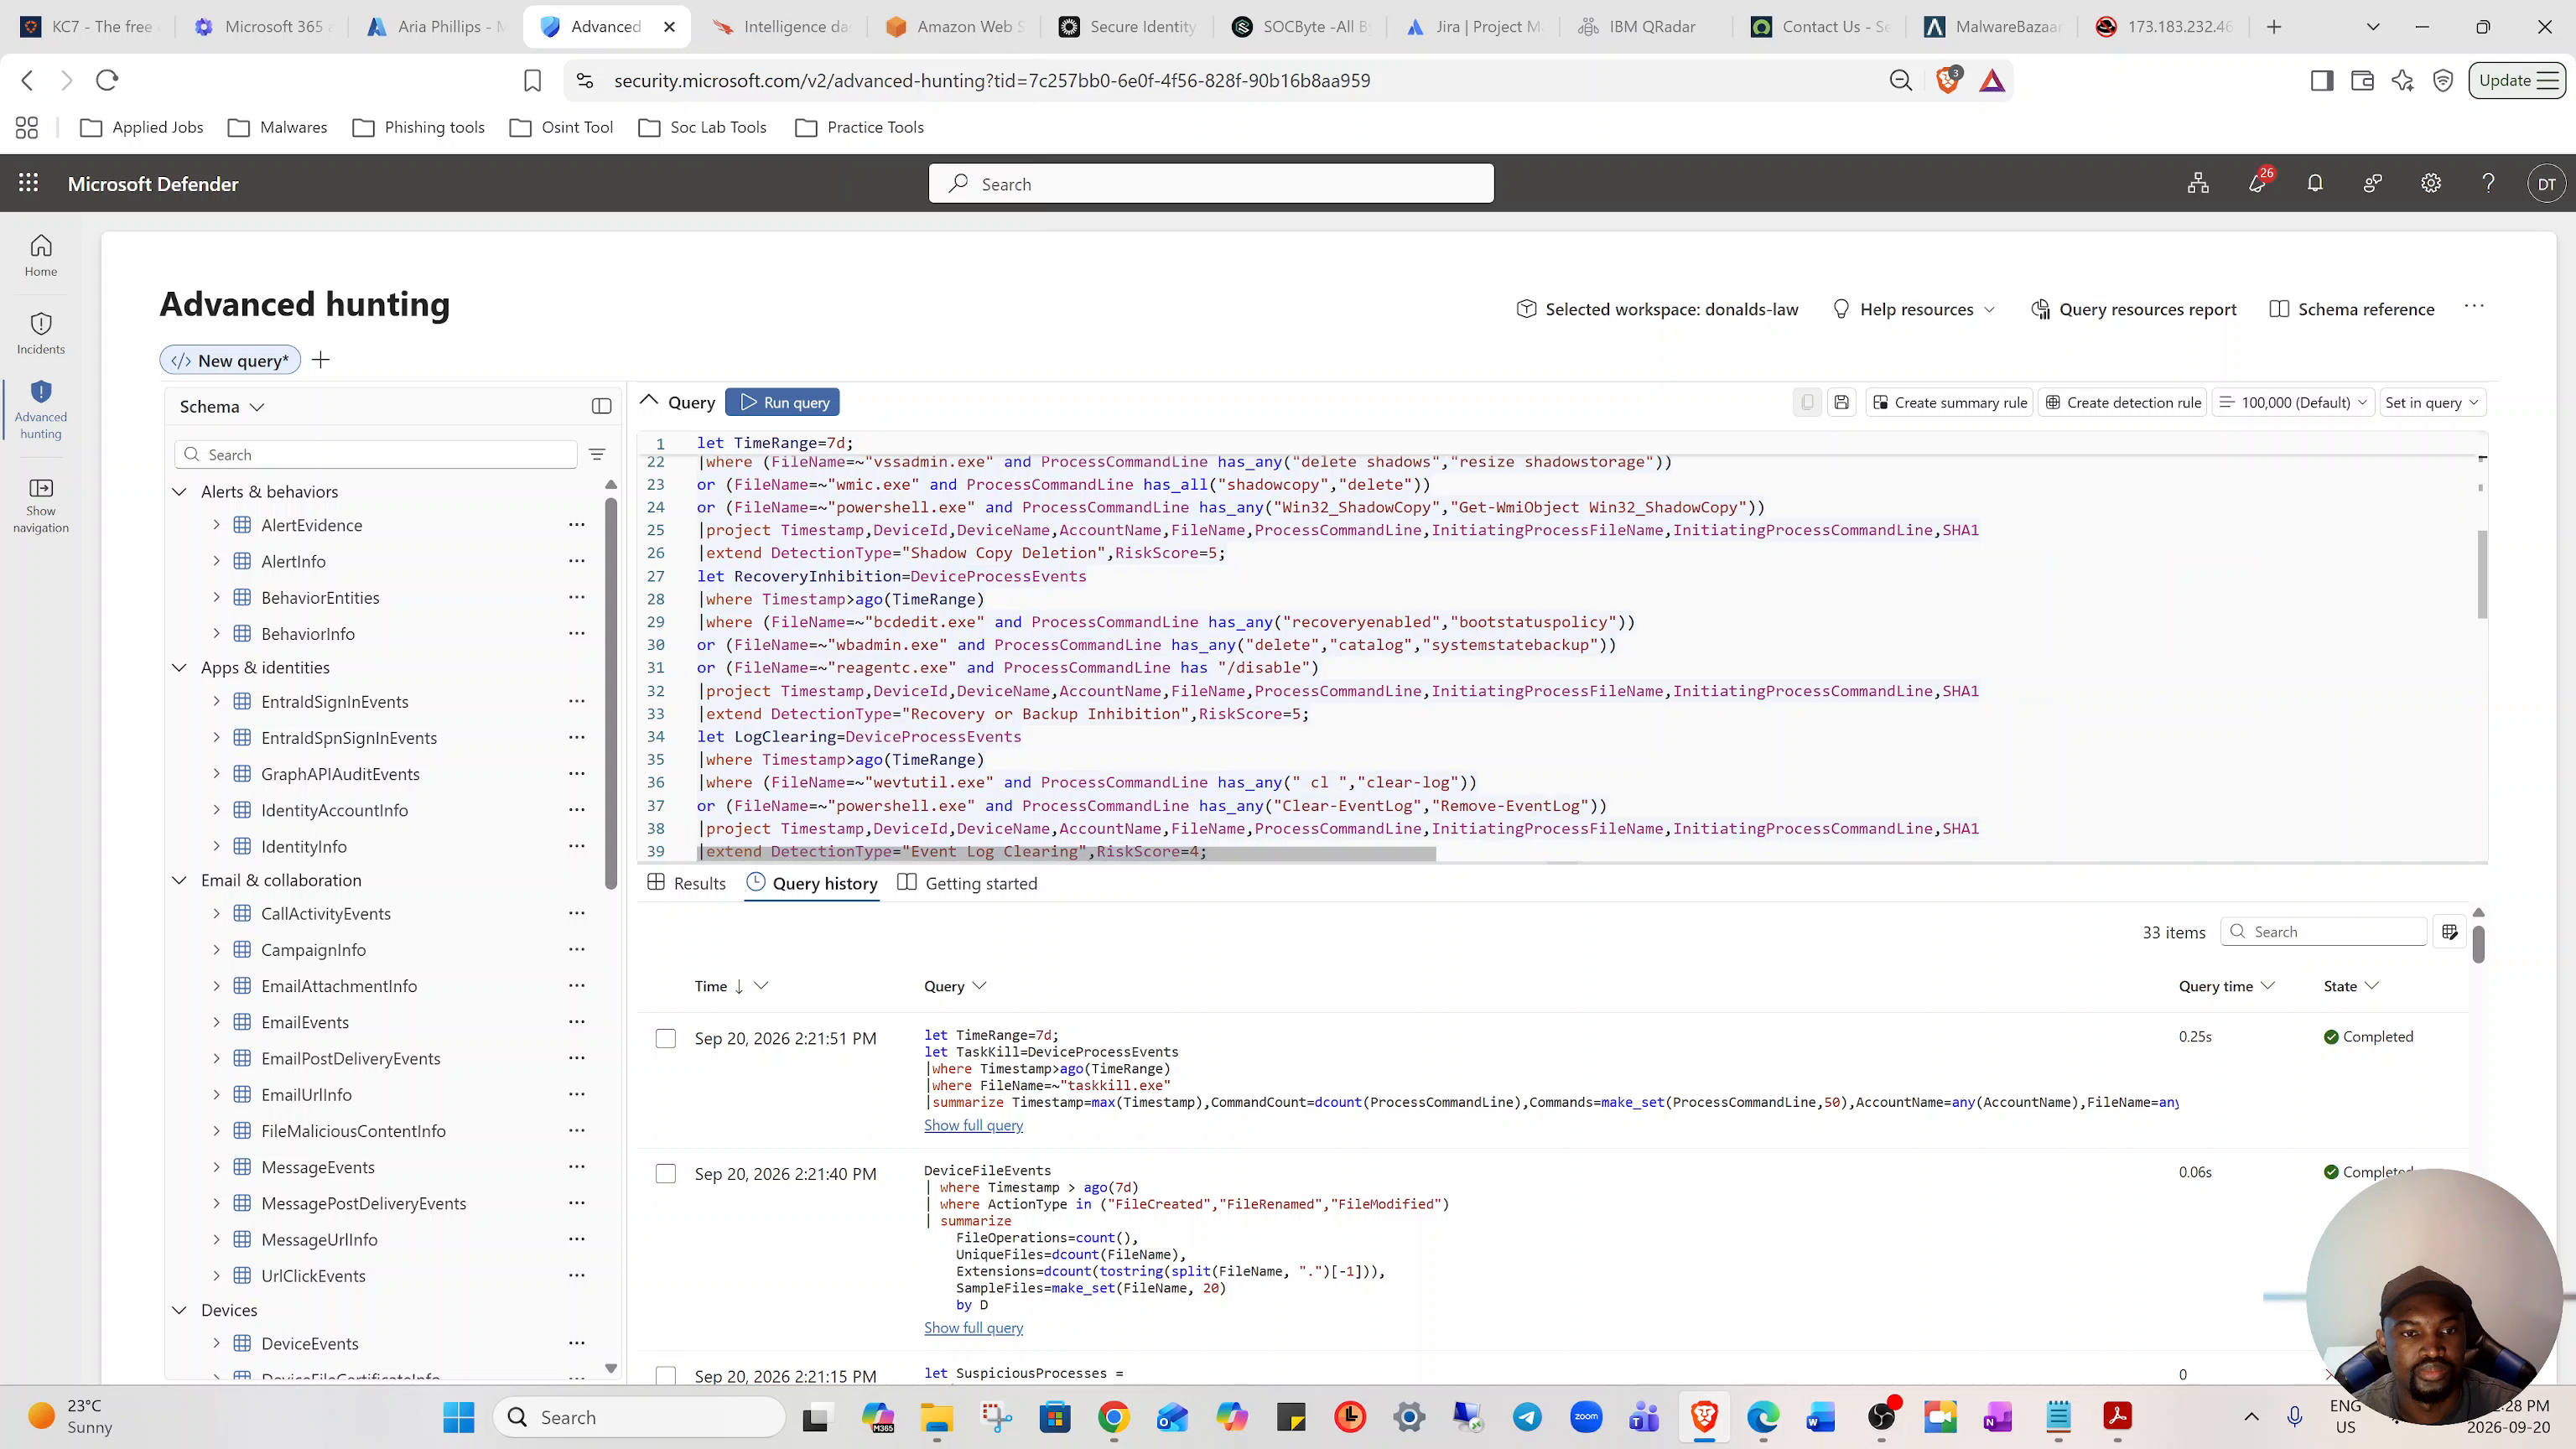
I used Microsoft Defender Advanced Hunting to review file, process, network, URL-click, and identity telemetry for connected behavior that can precede encryption.
Click to view Hunt 02 evidence ↓
Ransomware Precursors → Endpoint & Identity Hunt
I used Microsoft Defender Advanced Hunting to review file, process, network, URL-click, and identity telemetry for connected behavior that can precede encryption.
Define precursor behaviors → search process, file, network, and identity telemetry → correlate sequences → scope hosts and users.
Review connected activity rather than relying on one IOC: suspicious execution, remote access, defense evasion, recovery inhibition, and rapid file activity.